AvastSvc.exe keeps adding "gen-webserver.local" to hosts file

Hi everyone,

I’ve noticed something odd with my Windows hosts file recently. An entry for gen-webserver.local keeps appearing out of nowhere, and I’m pretty sure Avast is behind it.

I ran Process Monitor to track down what was modifying the file, and the logs point directly to AvastSvc.exe. Here’s a snippet of what I captured:

08:49:31.9045476	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,151, Length: 81, Priority: Normal
08:49:31.9077107	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,232, Length: 2, Priority: Normal
08:49:31.9079909	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,234, Length: 103
08:49:39.5613875	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,151, Length: 81, Priority: Normal
08:49:39.5629975	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,232, Length: 2, Priority: Normal
08:49:39.5631528	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,234, Length: 103
08:51:26.6864544	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,151, Length: 81, Priority: Normal
08:51:26.7065280	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,232, Length: 2, Priority: Normal
08:51:26.7067785	AvastSvc.exe	3552	WriteFile	C:\Windows\System32\drivers\etc\hosts	SUCCESS	Offset: 8,234, Length: 103

For reference, here’s my system info:

OS Name:                       Microsoft Windows 11 Pro
OS Version:                    10.0.26200 N/A Build 26200
OS Manufacturer:               Microsoft Corporation
OS Configuration:              Standalone Workstation
OS Build Type:                 Multiprocessor Free

And the Avast version I’m currently running:

DisplayName    REG_SZ    Avast Free Antivirus
DisplayVersion    REG_SZ    26.7.11086.3745

As you can see, AvastSvc.exe is writing to the hosts file repeatedly within a short timeframe. The entry being added is gen-webserver.local.

Has anyone else experienced this? I’m not sure if this is part of some Avast feature (like Web Shield, a local network scanner, or perhaps a captive portal detection mechanism) or if it’s something I should be concerned about.

A few questions:

  • Is this expected behavior from Avast?

  • If so, what is the purpose of adding gen-webserver.local?

  • Can this be disabled without turning off core protection features?

Any insights would be much appreciated. Thanks in advance!
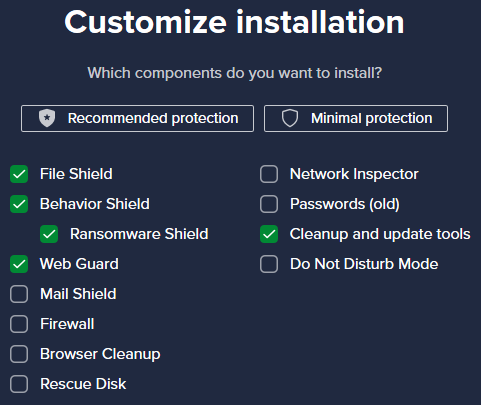
It’s probably not Web Guard (new name for Web Shield).

I only have File Shield, Mail Shield, and Web Guard installed, and I don’t have any weird entries in my Win 11 host file.

Just to add a bit more context – I have three laptops running the exact same Windows build and Avast version. All three are configured with the same set of components (please see the attached screenshot for reference).

To rule out any local anomalies, I ran a simple test:

- Removed the gen-webserver.local entry from the hosts file on all three machines.

- Rebooted each laptop.

In all three cases, the entry was automatically re-added after the reboot. This behaviour is consistent across every machine, which suggests it’s not a one-off glitch but something deliberately triggered by Avast – most likely during startup or service initialisation.

This makes me even more convinced that AvastSvc.exe is intentionally writing this entry, but I’m still unclear on the purpose behind it.

Here’s another test scenario I ran:

  • Removed the gen-webserver.local entry from the hosts file.
  • Uninstalled/removed the Web Guard component from Avast.
  • Rebooted the system.

After this, the entry no longer gets added to the hosts file.

This seems to confirm that the Web Guard component is responsible for writing this entry.

Has anyone else tested this or can confirm similar behaviour?

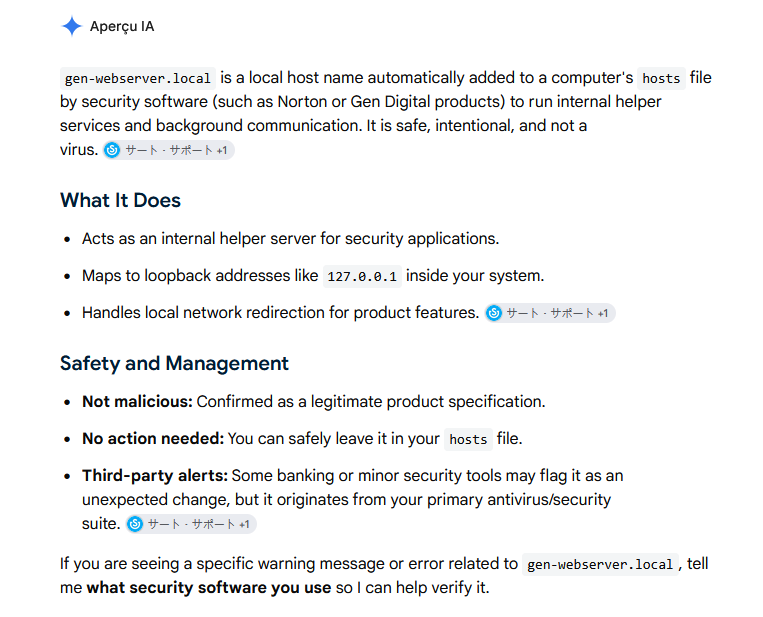
Some clarifications from the AI regarding these entries in the hosts file:

nb:avast is a part of Gen Digital :wink:

As for my three Windows devices, none of them added this line to my hosts files… Maybe because they’re write-protected???

That said, if that’s the case (Avast’s intention to better protect us), it would be good if that were mentioned in the terms of use (EULA).

edit:That said, if that’s the case (Avast’s intention to better protect us), it would be good if this were mentioned in the terms of use (EULA).
It’s possible that this only applies to certain regions (due to legal considerations).
Please specify your region; as for me (just to clarify, I’m not affected), it’s the EU.

1 Like

Avast Secure Browser has now it’s own AI Chat function, it’s called Smart Chat. So I asked them what gen-webserver.local does (I’ve translated the dutch version with Deepl):

What exactly does this mean?
The .local extension is used by mDNS (multicast DNS, also known as Bonjour or Avahi).
This allows devices on your home network or local network to find each other automatically without the need for a central DNS server.
So it’s not a website on the internet, but a device or service on your own network.

gen-webserver.local is:

A web server running on a device on your network (e.g., a Raspberry Pi, NAS, smart home hub, or a program on your computer).
This may be related to software from Gen Digital (Norton, Avast, AVG, etc.), which sometimes launches a local web server for its management interface or dashboard.
It could also simply be a name you (or a program) have assigned to a local web server.

The Windows region details are as follows:

D:\Download>systeminfo | findstr /B /C:“System Locale”
System Locale: zh-cn;Chinese (China)

D:\Download>reg query “HKCU\Control Panel\International\Geo” /v Name

HKEY_CURRENT_USER\Control Panel\International\Geo
Name REG_SZ US

I also have following entry in my (heavily edited) hosts file.

127.0.0.1 gen-webserver.local www.gen-webserver.local # gen digital helper server
127.0.0.1 revocation.gen-webserver.local www.revocation.gen-webserver.local # gen digital helper server

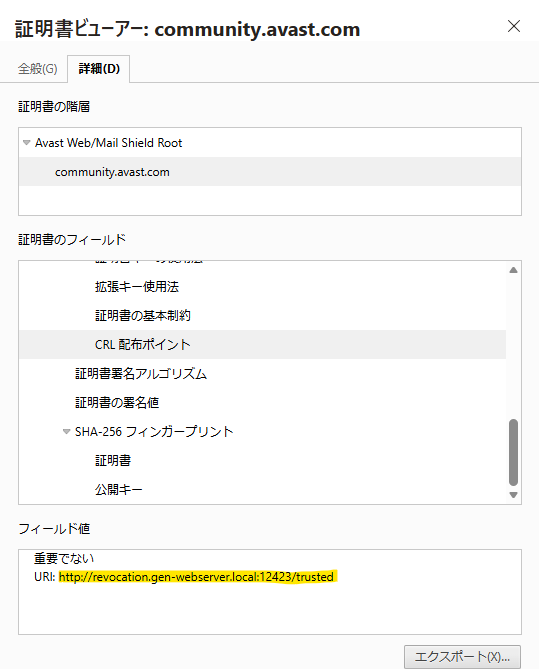
The second part “revocation.gen-webserver.local” rings a bell for me, and it indeed seems to be a part of Web Guard (Web Shield) and found as a CRL endpoint for Man-In-The-Middle TLS certificate.

Hi @dtcm9527 ,

I can confirm that, in some cases, Avast may temporarily add entries to the Windows hosts file when certain web protection features are enabled.

Examples of possible entries:
127.0.0.1 gen-webserver.local www.gen-webserver.local # gen digital helper server
1.2.3.4 redirector.gen-webserver.local www.redirector.gen-webserver.local # gen digital helper server
127.0.0.1 revocation.gen-webserver.local www.revocation.gen-webserver.local # gen digital helper server

These entries support specific Avast browser-security functions, such as Web Guard (formerly Web Shield) warning and related protection experiences. They are limited to Avast-controlled destinations used by those features and are not used to redirect your normal browsing to unrelated third-party websites.

Because some security tools monitor the hosts file for unexpected changes, you may occasionally see an alert when Avast adds or removes these entries. If the change relates to a Avast-managed entry associated with this feature, the behavior is expected and does not by itself, indicate that your device is compromised.

When the relevant feature is disabled or no longer active, Avast removes the associated entries.

2 Likes

Hi @prokopes ,

Thanks for confirming.

After updating to the very latest build I now also have two entries in my hosts-file.

127.0.0.1 gen-webserver.local www.gen-webserver.local # gen digital helper server
127.0.0.1 revocation.gen-webserver.local www.revocation.gen-webserver.local # gen digital helper server

I’ve been monitoring this for a few days now and the gen-webserver.local entry seems to be gone for good.

I didn’t change any Avast components, so I’m guessing Avast may have rolled out a background update or tweaked their policy on their end. Looks like it’s been resolved silently.

Just checked. My hosts-file still has the two entries from above.

Version: 26.7.11086g (build 26.7.11086.990)

So I’ve got another update on the gen-webserver.local saga.

Today, the entry showed up again:

Two laptops – around 4:50 PM

One laptop – around 1:40 PM

And here’s the kicker – no reboots on any of them. So this isn’t just a boot-time thing. Avast is definitely adding this entry during normal operation, probably as part of some periodic check or update.

I haven’t touched any settings since my last post.

Where did you see that this was linked to an update or occurred after a restart?

The fact that these entries appeared following the latest update does not mean that it is the update that is modifying the hosts file.

According to prokopes’ explanation, Avast may temporarily add entries to the Windows hosts file when certain web protection features are enabled.

He also states that these entries support, for example, WebGuard warnings, which are real-time warnings and can therefore occur at any time of day – not just at start-up or after an update.

Finally, he states that Avast adds or removes entries, but also that ‘When the relevant feature is disabled or is no longer active, Avast removes the associated entries’.
All of this clearly indicates that these entries are likely to appear and disappear several times a day.

You should expect to see these additions and removals in future.

1 Like

I’ve been using Process Monitor to track the hosts file and identify which process is writing to it.

Here’s what I observed:

13 Aug (before shutdown) – the gen-webserver.local entry was present in the hosts file.

14 Aug (~9:00 AM, after boot-up) – the entry was gone.

14 Aug (~4:50 PM) – the entry reappeared.

In all environments, the WebGuard component was enabled throughout this period.

I understand that Avast/WebGuard may add or remove entries as part of its normal operation. However, what caught me by surprise was that this behaviour is not documented anywhere in the official Avast knowledge base or release notes – at least not that I could find.

That’s the main reason I started this thread – to see if others have experienced the same and to hopefully get some clarification from the community or Avast team.

prokopes already clarified it fully as chris… stated. Also I don’t think any antivirus publicly “documented” every piece of their behavior; even the explanation by prokopes itself is kind of generous one imo.

2 Likes

And luckily so.

The whole point of a security tool is to check deep down into the devices it monitors.

So, I understand why prokopes’ information remained general; indeed, as NON said, the information provided is already quite generous.

We’re not talking about the functions of word processing, image editing or spreadsheet software, but about security software where certain details (even the act of discussing them) are already an open door for those seeking to compromise security.

If we suspect that security software is hiding things from us, there is no longer any reason to trust it; we should look elsewhere :wink:

I would add that it was reasonable to be concerned at first – the entries might have been suspicious – but since prokopes has confirmed that these entries are legitimate, without going into too much detail, that is the key point that should allow us to move on.