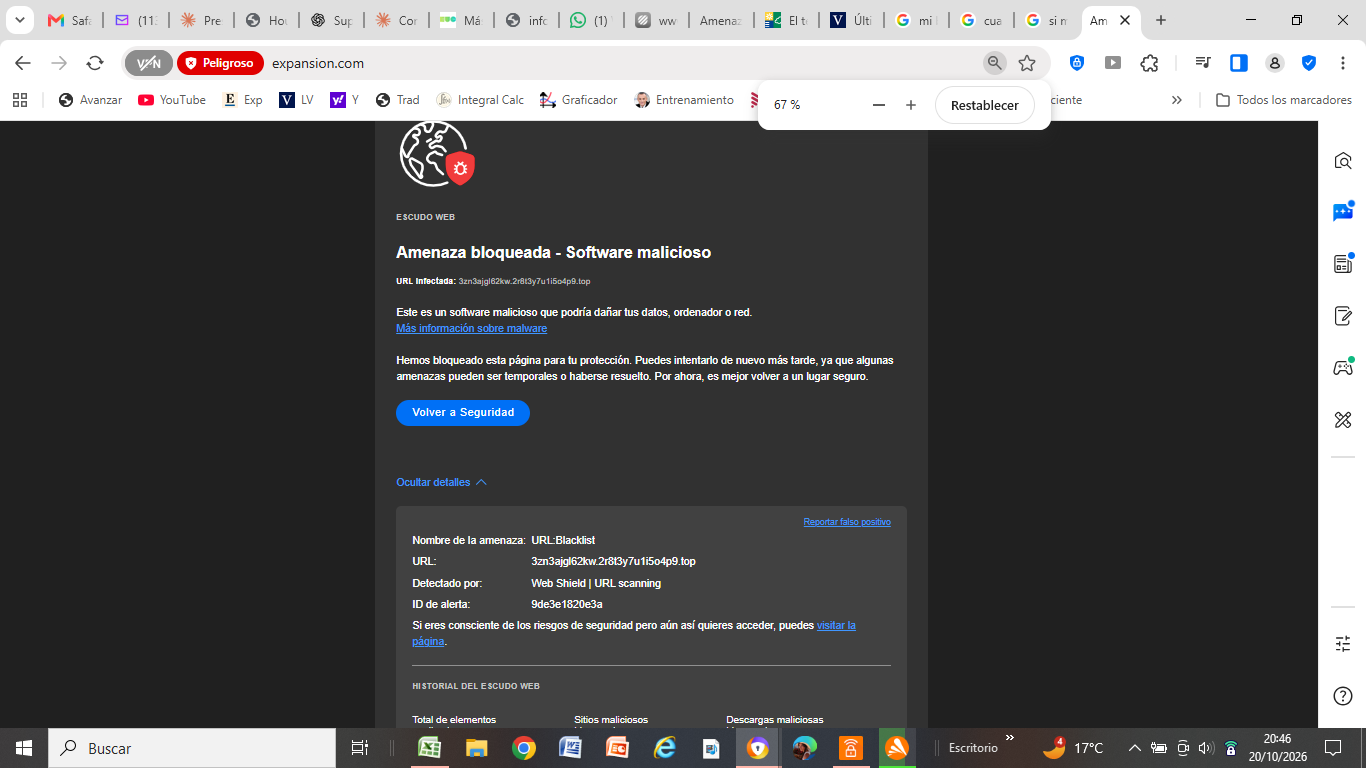
Subject: Persistent URL Detection – otakegypt.com, Webmail and WordPress Admin
Domain: otakegypt.com
Detection: URL
Alert ID: ba9d550a7dbc/2026-10-18T08:31:45.808Z
Affected URLs:
-
hxxps://otakegypt[.]com/
-
hxxps://www[.]otakegypt[.]com/
-
hxxps://webmail[.]otakegypt[.]com/
-
hxxps://otakegypt[.]com/wp-admin/
Hello Avast Community and Threat Labs Team,
I am the IT Manager at Otak Trading & Engineering in Egypt. Our corporate website, webmail, and WordPress administration page are being blocked by Avast Web Guard with a URL detection.
We have submitted multiple false-positive reports through the official Avast submission form, but the detection remains active. We understand that these submissions may not generate a direct response, so we are seeking assistance in bringing this case to the attention of the appropriate team.
Troubleshooting and investigation performed:
-
Our hosting provider, ChemiCloud, performed an Imunify360 scan of the hosting account and reported no detected malicious activity or scripts.
-
ChemiCloud confirmed that the SSL certificate is valid and properly installed.
-
The hosting provider reviewed WordPress core integrity and reported no suspicious activity in its latest investigation.
-
The website is accessible using Microsoft Defender and Avira, while Avast and AVG block it.
-
On a separate Windows device, the website was accessible before Avast was updated. The URL warning appeared after the Avast application and protection definitions were updated.
-
Adding a local exception in Avast restores access to the affected URLs.
-
FortiGuard previously confirmed a category update to Business for http://www.otakegypt.com/ on October 15, 2026.
We are continuing our investigation with the hosting provider and website developer. Some additional directories and older WordPress installations are being reviewed to confirm their purpose and ensure that no further remediation is required. We do not want to assume the detection is a false positive without completing these checks.
Request:
Could a moderator or Avast Threat Labs representative please help escalate this case for a manual review?
We would appreciate clarification on:
-
What specifically triggers the URL detection.
-
Whether the detection is associated with the root domain, the www hostname, the webmail subdomain, the WordPress admin path, or a specific resource loaded by these pages.
-
Whether any additional remediation is required on our side.
-
Whether the detection can be reassessed once the review is complete.
This issue affects more than 150 corporate Windows devices running Avast Free Antivirus. Manual exceptions are not a practical long-term solution.
Thank you for your assistance.
Kind regards,
Adel
IT Manager
Otak Trading & Engineering